
Officials and corporate leaders have dismissed recent critical infrastructure disruptions as routine, but security experts warn that hasty conclusions may mask potential cyber threats.
Federal officials and major private institutions have characterized a string of recent critical infrastructure failures as isolated technical glitches, a stance that has drawn criticism from security experts who warn that such rapid assurances may overlook evidence of malicious activity.
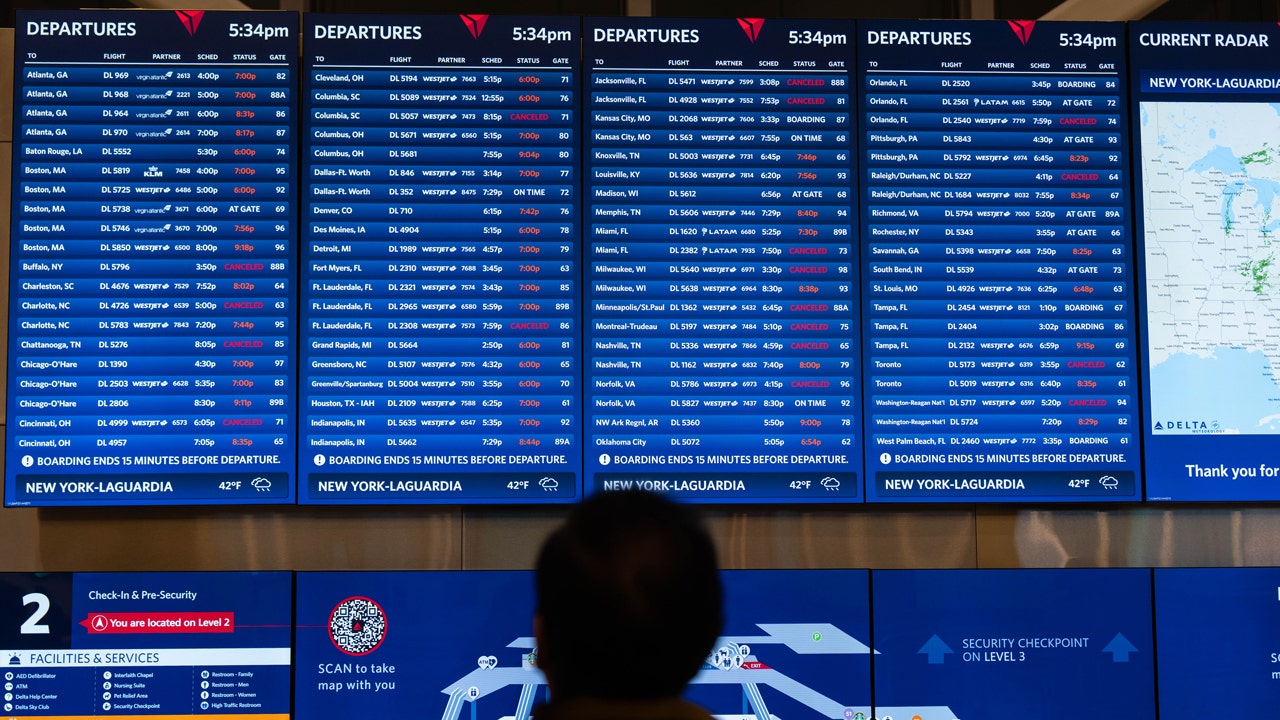
Over the past week, the United States experienced multiple high-profile service disruptions, including a nationwide ground stop that halted air travel, significant banking outages at JPMorgan Chase and other lenders, and service interruptions at Microsoft. Despite the operational impacts, officials have consistently maintained that the events were not the result of a cyberattack. Homeland Security Secretary Markwayne Mullin stated that the homeland and banking systems remained secure, while Director of National Intelligence Jay Clayton testified Wednesday before the House Homeland Security Committee that intelligence showed the outages were not coordinated or state-sponsored, attributing them instead to routine system maintenance and software upgrades.
Danny Cooper, CEO of the critical infrastructure security firm SMET, argues that the speed with which these assurances were issued is problematic. “A blanket statement like ‘there’s no malicious activity associated with any of the outages’ is almost impossible from a probability perspective,” Cooper said. She noted that public skepticism is understandable given that several critical systems faltered within a narrow five-to-six-day window. “How plausible is it that all these pillars or whatever all suffered major independent technical failures within a five- or six-day window? I think highly improbable,” Cooper said.
Cooper cautioned that definitive statements issued before comprehensive forensics can be completed may skip essential investigative steps. She argued that ruling out foul play without a full audit of affected environments could allow sophisticated adversaries to remain undetected. While acknowledging that organizations frequently undergo maintenance, Cooper warned that these periods are also susceptible to exploitation. “If it’s possible that they are using those software updates or upgrades or patches and in those moments actually injecting malware and exploits and so on,” she said. “On the physical side, being able to fully interrogate what has happened in the environment, who was there, and so on about what is happening in the periphery and what led up to that moment in time, those things take time.”
The official messaging surrounding the disruptions has also become a subject of political friction. The Democratic National Committee (DNC) recently voiced concerns regarding conflicting explanations from the current administration. Kendall Witmer, the DNC’s deputy communications director, alleged that the administration has provided inconsistent statements, citing an instance where Secretary Mullin suggested that artificial intelligence—referred to by the administration as “SI”—played a role in the disruptions. Witmer noted that this explanation appeared to contradict a subsequent stance from Secretary of State Marco Rubio, who reportedly declined to attribute the outages to AI.
As the debate continues, the tension remains between the government’s efforts to calm public anxiety through prompt explanations and the professional consensus that thorough forensic investigation is required to definitively rule out cyber threats, ensuring that potential vulnerabilities are not left unaddressed.

