
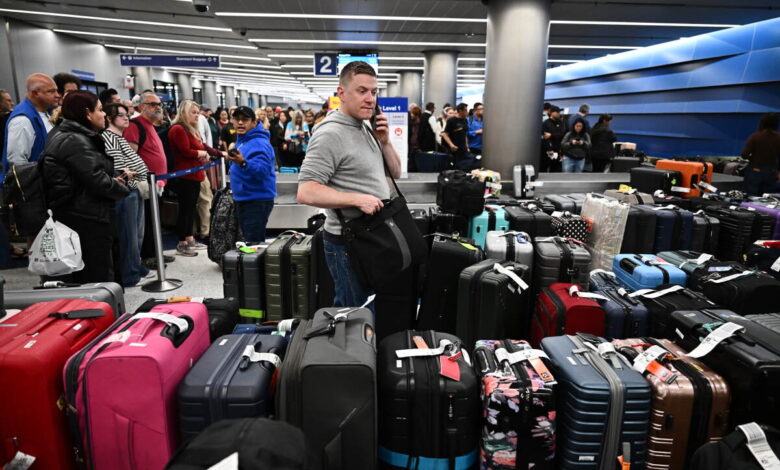
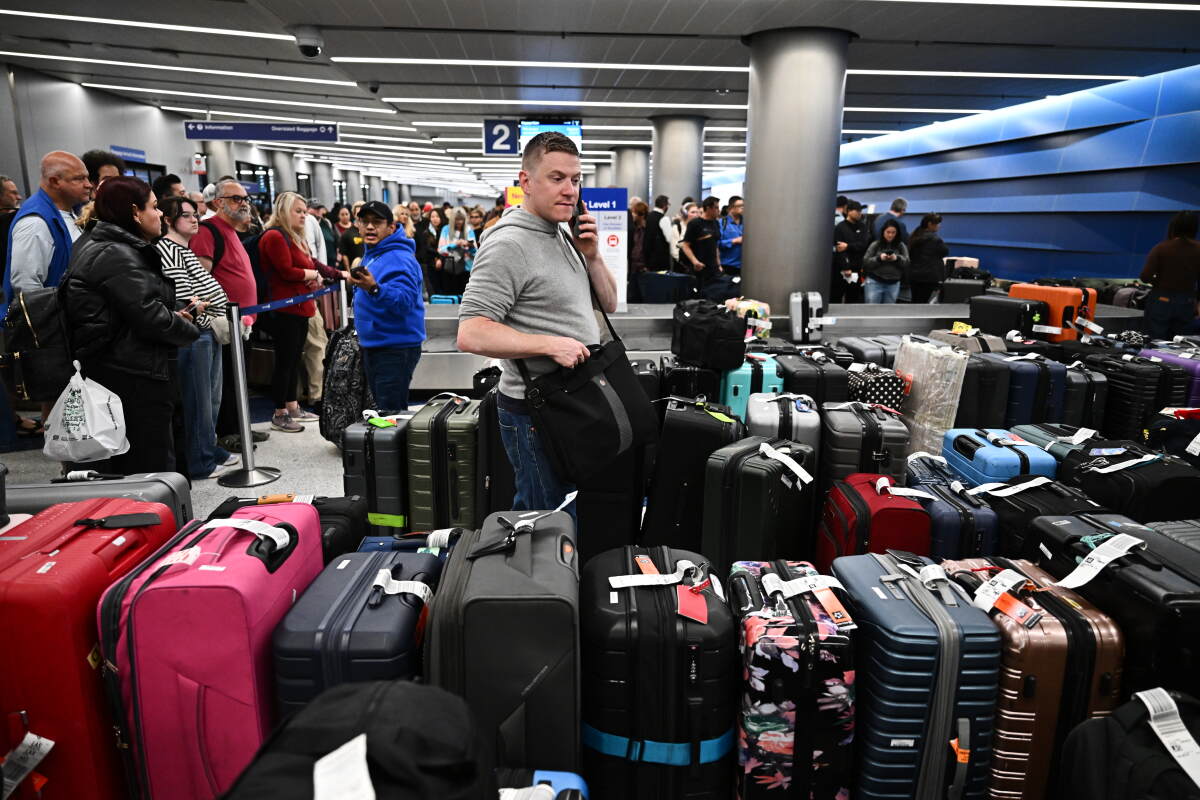
A rapid succession of technology failures across critical U.S. infrastructure over the past several days has sparked urgent demands for accountability and heightened concerns regarding the nation’s cyber security posture.
The wave of disruptions began with Microsoft email systems and a nationwide grounding of flights by the Federal Aviation Administration. Subsequent outages impacted JPMorgan Chase banking services, Apple, Marriott International, and the National Security Agency’s classified internal communications network. Government officials and corporate representatives have attributed the individual incidents to routine technical issues, such as faulty software updates, server load conditions, and system misconfigurations.
President Trump, while attending an international summit in Manila, dismissed concerns over the stability of the affected systems, telling reporters, “It’s fine.” Similarly, Director of National Intelligence Jay Clayton stated that the outages were not the result of a coordinated cyberattack or nation-state action, characterizing them instead as the outcome of institutions upgrading vulnerable legacy systems.
However, security experts have challenged these assurances, noting that the frequency and scale of the disruptions suggest deeper, systemic vulnerabilities. Marcus Rogers, director of the Cyber Forensics Lab at Purdue Polytechnic Institute, warned that the “muddy picture” presented by six separate infrastructure failures in a single week is “alarming.” Rogers argued that even if the causes are rooted in human error or routine maintenance, such easy failures highlight the susceptibility of critical systems to potential targeted attacks.
“There’s something wrong in the system itself and we can’t ignore that,” Rogers said. He further criticized the inconsistent messaging from affected companies, noting that public claims denying a cyberattack are often made before the root cause is confirmed.
Senate Intelligence Committee ranking member Mark Warner (D-Va.) suggested that artificial intelligence is complicating the security landscape by allowing vulnerabilities to be identified and exploited at unprecedented speeds, placing extreme pressure on organizations to patch systems rapidly. Herbert Lin, a senior research scholar at Stanford University’s Center for International Security and Cooperation, emphasized that while a common agent behind the failures seems unlikely, it cannot be entirely ruled out. “Buying more complexity, that means you’re buying more vulnerability,” Lin stated.
As public anxiety grows, some officials have called for greater transparency. Republican lawmakers have requested a formal briefing from the Trump administration regarding the NSA incident. Meanwhile, California Governor Gavin Newsom stated that the state is addressing AI risks independently due to a lack of federal regulation, adding that the situation requires “mature leadership.”
These concerns arrive alongside warnings from the FBI and private intelligence firms regarding the rise of autonomous cyber threats. The FBI issued a FLASH advisory on Friday regarding the use of the ARTEX platform by malicious actors to automate intrusions at machine speed, while Google’s Threat Intelligence Group warned this week that the “era of autonomous attacks has arrived.” Additional reports from security researchers at Report URI indicated that malicious code was detected in Optimizely, a tool used by numerous major organizations to test website layouts, potentially exposing visitors to data theft.
As investigations into the individual outages continue, officials remain divided on the primary causes. Transportation Secretary Sean Duffy reported that the FAA had not yet reached a definitive conclusion regarding the root cause of the flight groundings, despite initial reports pointing to a router issue and data overload. With uncertainty lingering, experts urge the government and the public to reconsider the nation’s heavy reliance on complex, interconnected digital networks. Lin suggested that citizens take personal precautionary measures, such as maintaining cash reserves, acknowledging that the nation may have reached a “tipping point” with its current infrastructure.

