United States and international cybersecurity agencies issued urgent warnings on Wednesday regarding critical vulnerabilities discovered within the foundational computer programming language PHP, prompting some organizations to take their websites offline immediately. Officials and industry experts estimate that the security flaws could potentially affect up to 70 percent of the internet due to the language’s widespread use in web applications.
The National Security Agency, alongside cyber defense authorities in the United Kingdom, Australia, Canada, Japan, and several European nations, posted coordinated warnings on Wednesday. The PHP Foundation released software patches the same day, but governments stressed that organizations should take vulnerable systems offline to protect critical assets until the updates are fully applied.
The NSA stated on the social platform X that PHP vulnerabilities frequently provide a direct pathway to a server’s file system or database. The agency advised that if an immediate software update is not feasible, organizations should take the system offline until complete mitigation can be achieved. Germany’s cybersecurity agency, the BSI, described PHP as a central building block in web applications, while cloud security company Wiz noted in a blog post that the flaws could impact a vast majority of the internet given how many websites rely on the scripting language.
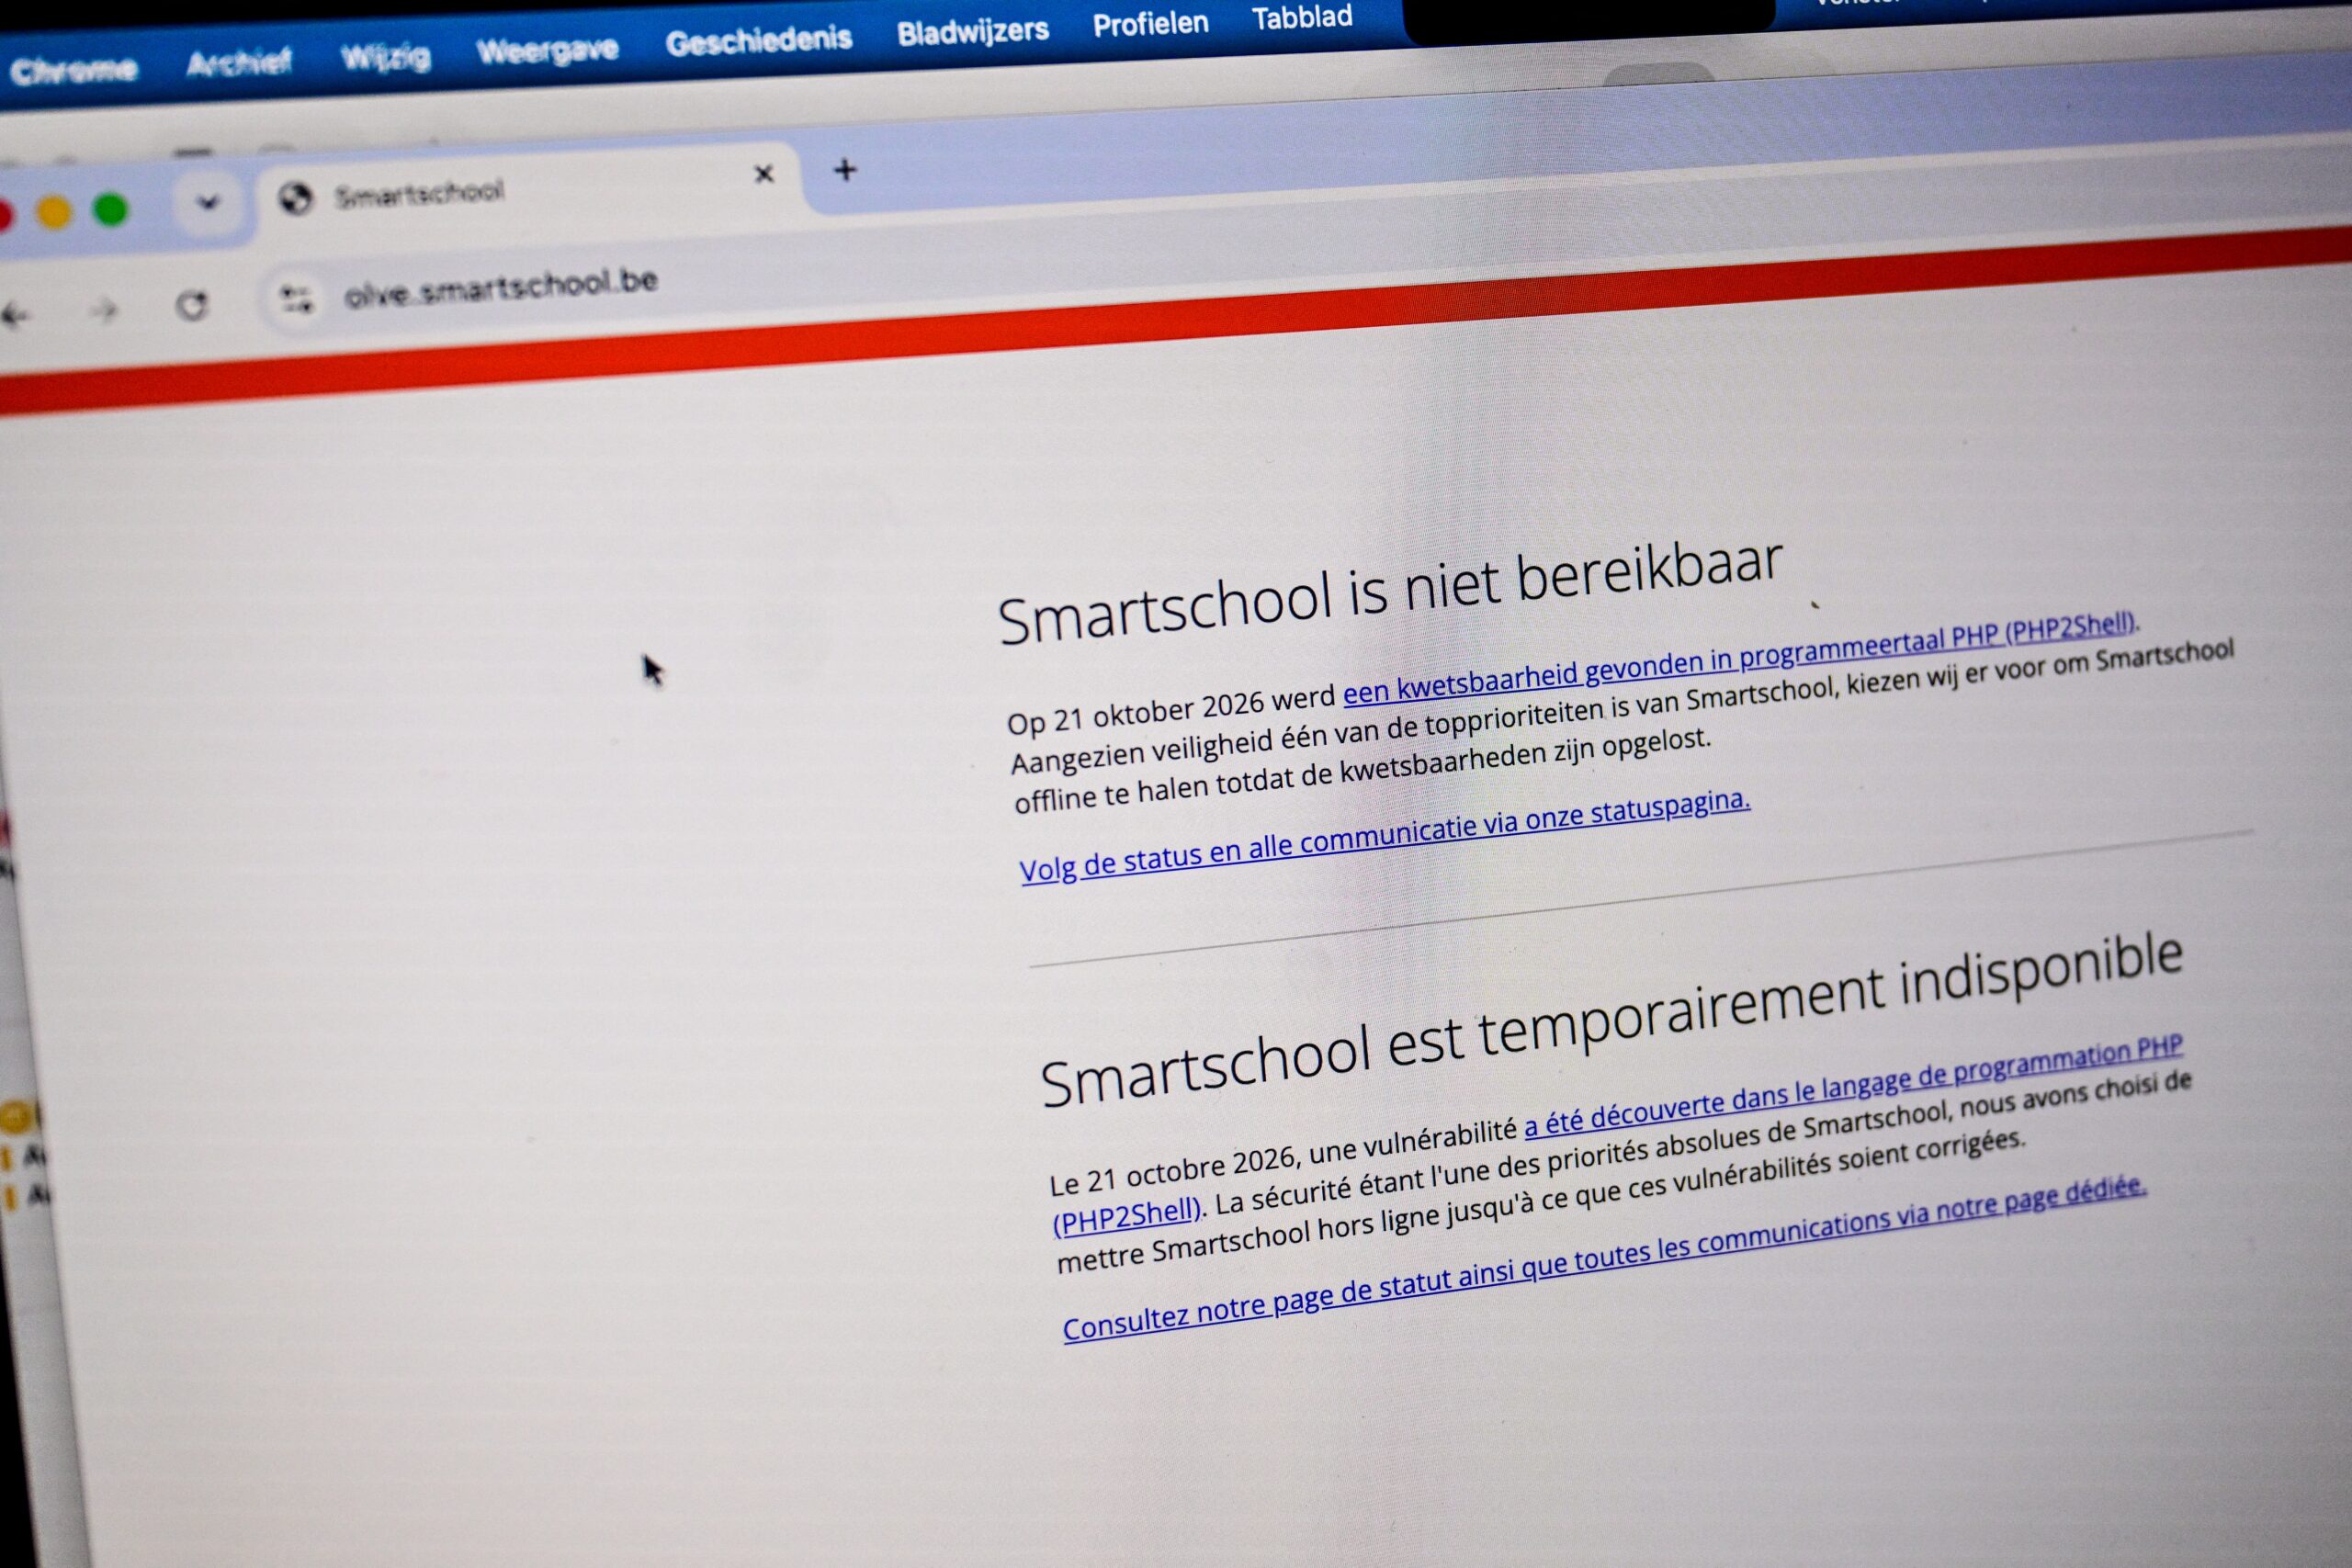
The international warnings resulted in immediate disruptions across multiple regions. Government and private websites were taken down on Wednesday in several countries. Affected entities included several Finnish and Dutch government websites, the Dutch and Belgian national cyber agencies, a French domain name organization, and the main homepage of the French tax portal.
Frontier artificial intelligence laboratory OpenAI revealed that it led a coalition of security groups and researchers over a two-month period to address the PHP flaws. The organization stated that its GPT 5.6-Sol AI model discovered the vulnerabilities. OpenAI characterized the issue as one of the most impactful security events in recent memory given the severity of the flaws and the widespread use of PHP. The lab also reported that, to its knowledge, the AI system found the vulnerabilities before malicious actors did, creating a vital defender’s window for maintainers and security providers to prepare fixes and protections prior to public disclosure.
Internet services organization Cloudflare, which collaborated with OpenAI in responding to the incident, warned that the vulnerabilities could enable cyberattacks, disrupt computer networks, or leak sensitive online data. Before patches were officially released, Germany’s BSI cautioned that attackers could succeed in executing massive attack campaigns and compromising IT systems across a wide array of application areas. BSI Vice President Thomas Caspers warned at the time that short-term, large-scale exploitation was highly likely.
Legal and cyber experts emphasized the gravity of the situation. JP Buckley, a partner at the law firm Lewis Silkin, remarked that instructing organizations to consider taking websites completely offline demonstrates the exceptional seriousness of the vulnerability. Ciaran Martin, the former head of the British cyber agency, described the issue on LinkedIn as very bad and requiring immediate attention.
The NSA announced plans to publish formal guidance on remediating the vulnerabilities shortly. Meanwhile, the U.S. Cybersecurity and Infrastructure Security Agency did not respond to requests for comment and had not issued a formal alert on the threat as of publication.