
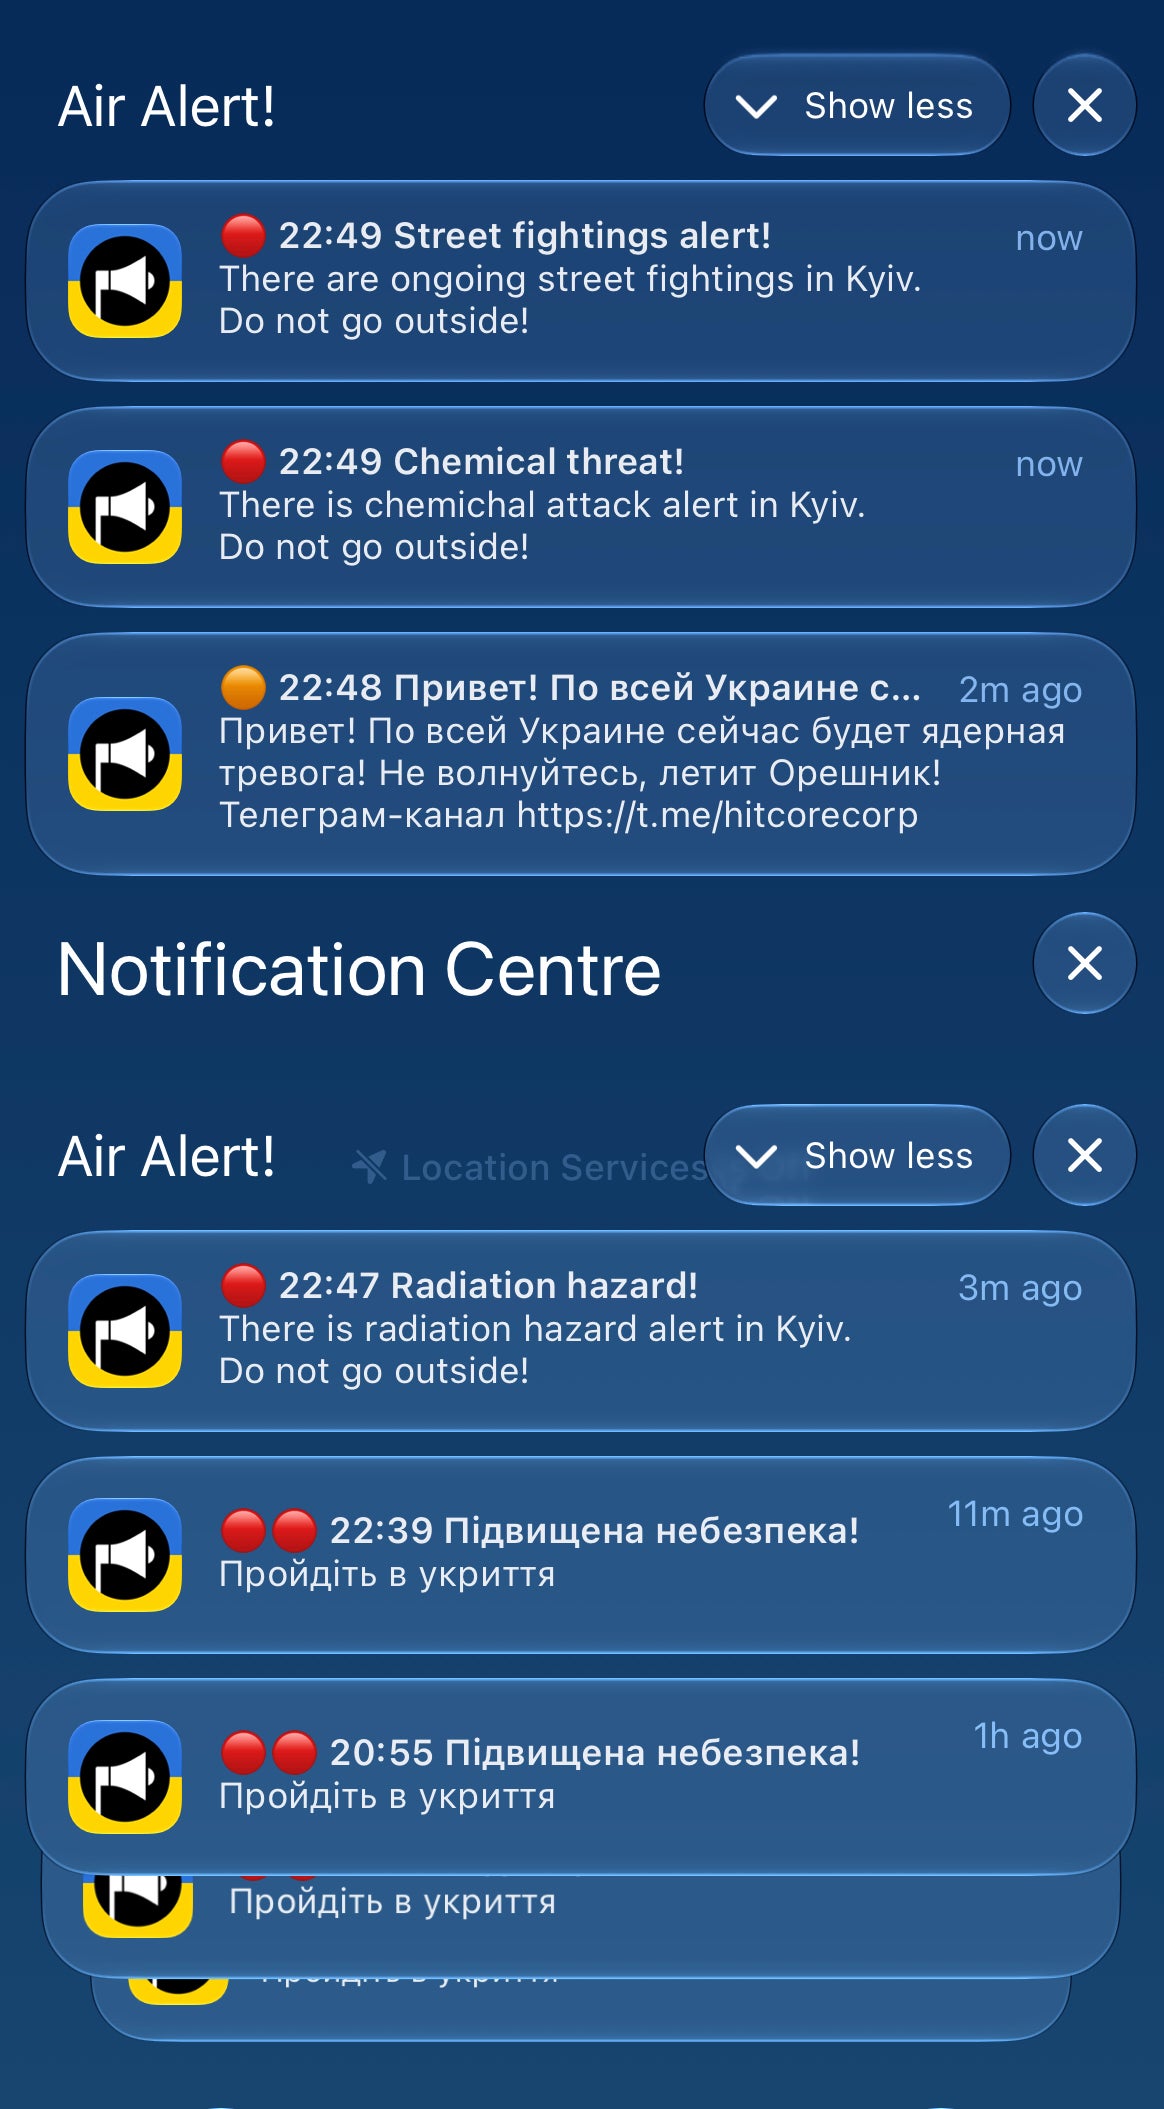
Millions of Ukrainians received alarming mobile notifications on a Sunday night warning of imminent radiation, chemical attacks, and street fighting in Kyiv through an official emergency alert application. The initial panic was swiftly followed by clarifying messages informing citizens that the application had likely been compromised by a hostile cyberattack and that no such threat existed. A subsequent update on Telegram reassured the public that there was no radiation danger and urged calm. Screenshots from the late-night alerts showed multiple warnings of increased danger, shelter directives, and references to nuclear threats.
Shortly after the incident in Kyiv, Russian state communications experienced a parallel disruption, with Russian citizens receiving warnings that Ukraine had hacked domestic systems to broadcast alerts about impending nuclear strikes. Neither government officially claimed responsibility for the respective breaches, and the exact origins remain technically unclear. However, analysts and officials widely interpret the sequence as a tit-for-tat digital exchange initiated by Moscow. A representative from the Ukrainian hacktivist community suggested to reporters that the breach of Russian alert systems served as a retaliatory operation.

Security officials report that digital warfare has escalated dramatically since the conflict began in February 2022. According to data released by Ukraine’s security service, the SBU, more than 16,000 Russian cyberattacks and critical digital incidents had been neutralized up to July of this year. Brigadier General Volodymyr Karasteliov detailed a massive three-hour distributed denial-of-service attack targeting a national television broadcaster, explaining that the botnet generated up to 200,000 requests per minute from global nodes across Europe, Asia, and the United States to overwhelm application servers.
Global threat data underscores a persistent digital imbalance between the warring nations. Research published in PLOS identified Russia as a leading global hotspot for cybercriminals, with Ukraine ranking second. Furthermore, telemetry from cybersecurity firm CybelAngel recorded 1,651 digital incidents directed at Ukrainian entities compared to 575 targeting Russian counterparts between January 2025 and January 2026, maintaining an asymmetry that analysts say mirrored previous annual trends.
Cybersecurity experts emphasize that targeting emergency communication channels carries a psychological intent that extends beyond mere technical disruption. Adam Pilton, a cybersecurity adviser at Heimdal, explained that compromising an air raid warning system exploits an immediate emotional vulnerability, generating panic much like a targeted phishing scam. When communication infrastructure tied directly to official government bodies is compromised, the primary casualty is public trust. Pilton noted that citizens rely on government channels differently than traditional media, assuming an inherent level of authenticity that makes such breaches exceptionally disruptive.
Despite assertions from Russian quarters that the targeted platforms function as general communication tools rather than active civil defense networks, experts argue that the operational intent is clear. Oleksandr Merezhko, chair of the Ukrainian parliament’s foreign affairs committee and a member of President Volodymyr Zelensky’s party, acknowledged the psychological toll while maintaining that the population remains resilient. Describing the incident as an unpleasant reality of modern warfare, Merezhko affirmed that Ukrainian citizens understand the risks and remain fully prepared to handle ongoing digital provocations.