
Heightened concerns over digital security are intensifying as a string of recent high-profile outages—spanning United Airlines, Apple Pay, and the Federal Aviation Administration—draw renewed attention to the vulnerability of critical infrastructure. While those specific incidents were not attributed to cyberattacks, security experts warn that the intersection of aging software systems and rapidly advancing artificial intelligence creates a fertile environment for malicious exploitation.
Cybersecurity firm VulnCheck reports that more than 100,000 vulnerabilities have been disclosed so far this year, a figure more than double that of 2025. Furthermore, the speed at which hackers exploit these weaknesses has increased by 33% compared to last year. Aaron Mitchell, CEO of the cybersecurity firm HeroDevs, notes that outdated software remains a primary target for attackers. According to Mitchell, approximately half of all known exploits target software versions that are no longer supported by their original maintainers.
“That’s where attackers see a big opportunity,” Mitchell said. “That’s an easy way for me to get access and start to do some real damage.”
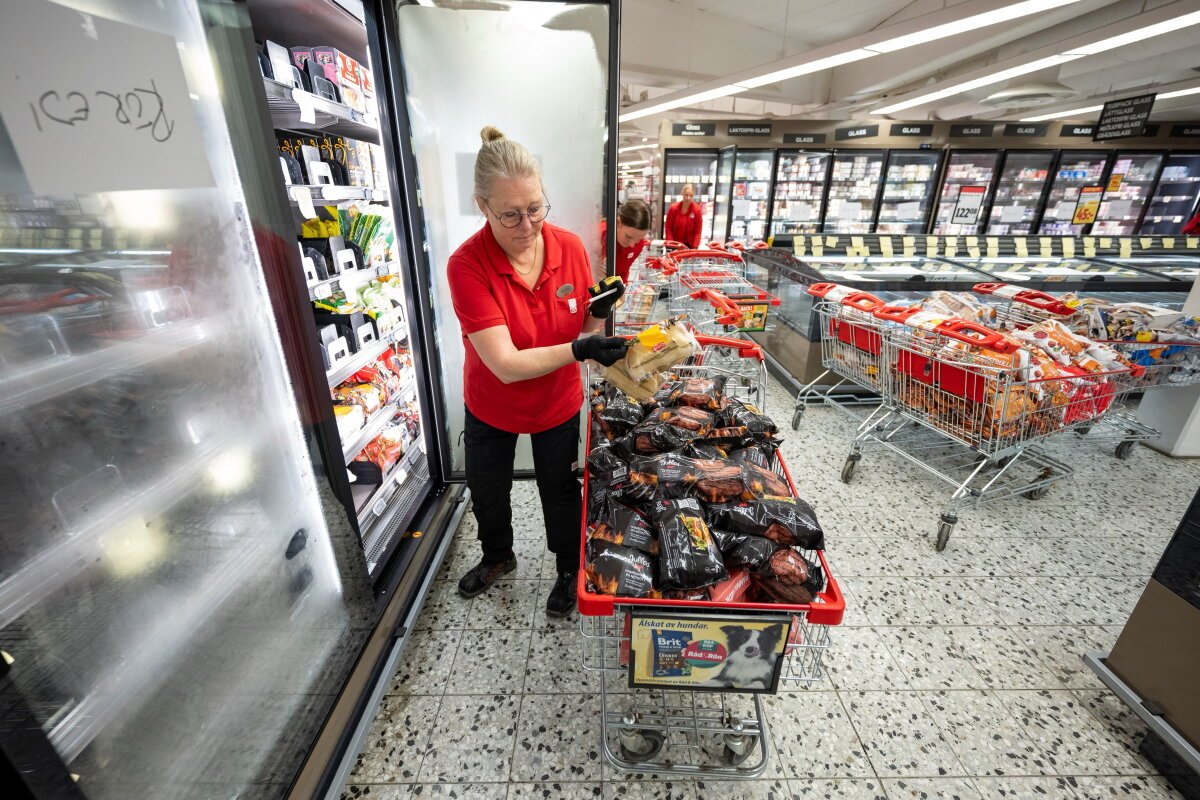
Recent global incidents illustrate the practical risks of legacy infrastructure. Earlier this month, hackers targeted supermarket refrigeration systems across seven countries, raising temperatures in freezers by exploiting vulnerabilities in outdated software. Similar tactics were attempted against French blood banks, though authorities successfully intervened before the systems were compromised.
AI is increasingly playing a role in this arms race. Last month, AI-driven discovery identified two significant flaws in the PHP programming language, which underpins more than two-thirds of the internet. The vulnerabilities could have allowed unauthorized remote access to web servers. While a patch was issued, reports indicated that some websites were exploited before they could be updated. Additionally, the recent disclosure of a critical vulnerability in Java, dubbed “Java4Shell,” forced a rapid response from companies worldwide to secure their systems.
Richard Horne, head of the UK’s National Cyber Security Centre, characterized the situation as a reliance on “vulnerabilities that have been tolerated for far too long.” While the exploitation of these gaps has not reached its full potential, Mitchell warned that the threat is mounting. “Every day that goes by, we get that much closer to the edge,” he said.
In Washington, the leadership of the federal government’s cybersecurity efforts is in transition following reports that President Trump’s National Cyber Director, Sean Cairncross, will be leaving his position. Cairncross opted not to serve an additional two-year term, leaving a key role vacant as officials grapple with these emerging digital threats.

