French cybersecurity authorities have confirmed that multiple remote refrigeration control systems were compromised in a string of targeted digital intrusions affecting supermarket display units across the country. The breach involved Danfoss AK-SM and AK-SC series controllers, alongside Copeland subsidiaries XWEB and Dixell XWEB monitoring systems. Danfoss stated that the majority of impacted hardware consisted of older legacy controllers, specifically naming the AK-SM 800 and AK-SC 355 models. While the Paris public prosecutor’s office has launched a formal investigation into the incidents, officials have not yet disclosed the identity of the attackers, the precise method of entry, or whether the perpetrators exploited known vulnerabilities.
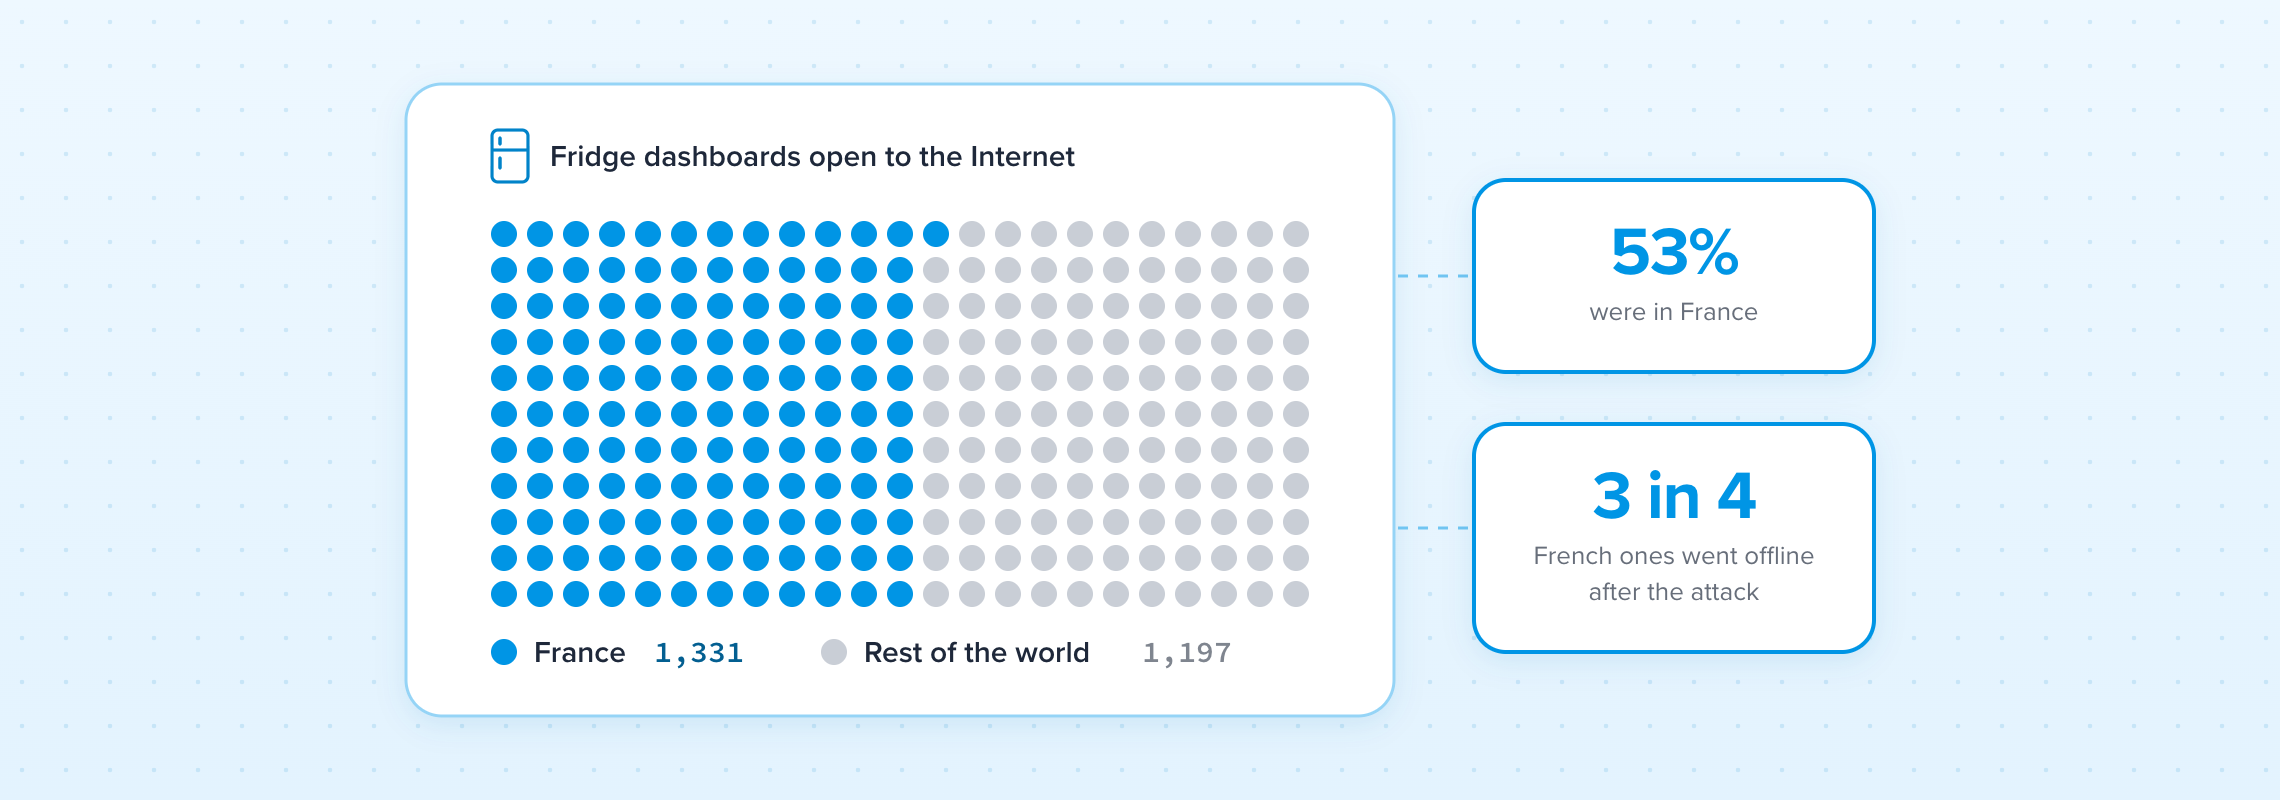
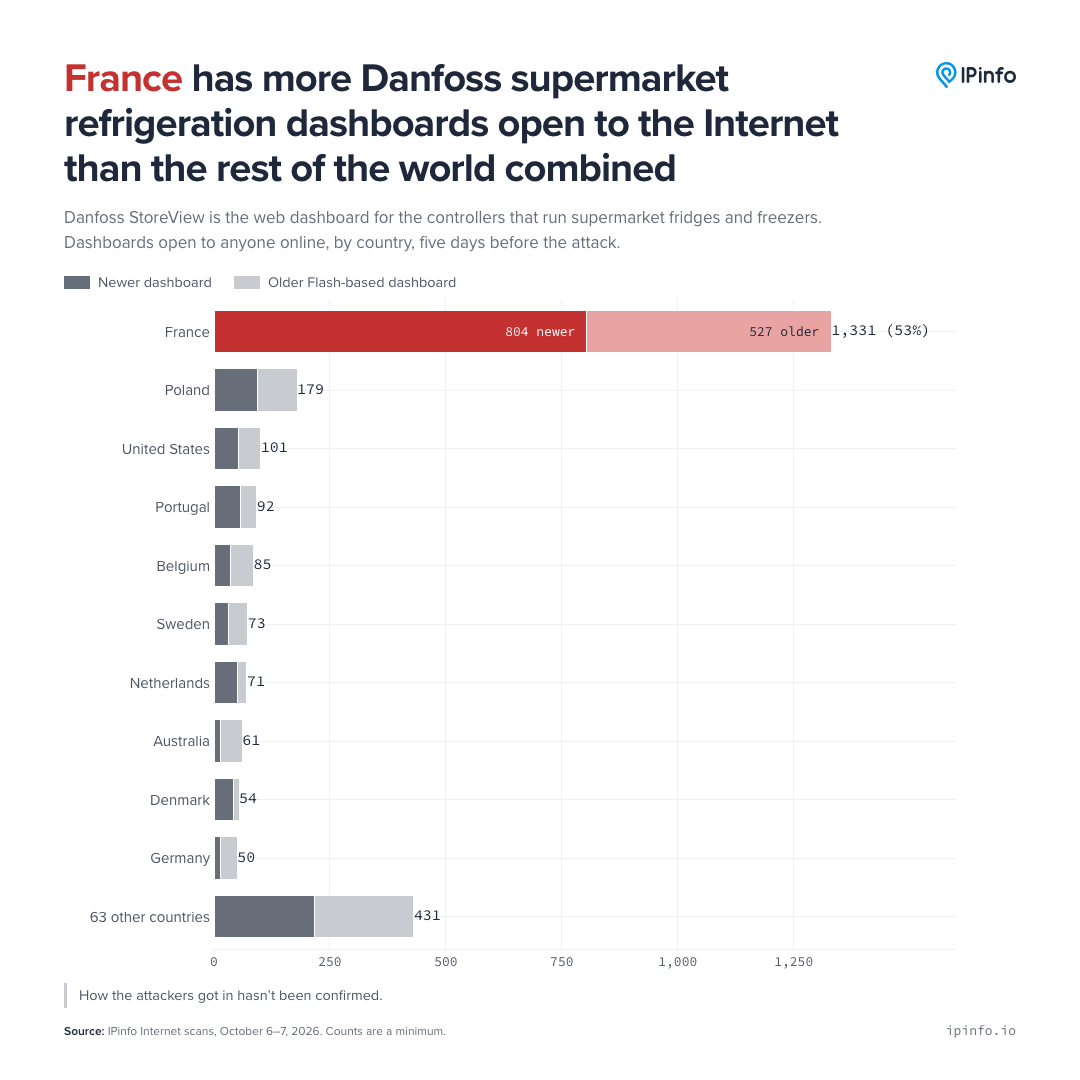
Ahead of the incidents, internet scanning records from IP address data firm IPinfo indicated a vast digital footprint for the hardware. Between October 6 and October 7, approximately five days before the temperature-alteration attacks came to light, global scans detected 2,528 Danfoss StoreView control panels accessible via the public internet. More than half of those devices—1,331 panels, accounting for 53% of the global total—were located in France. Poland ranked second with 179 exposed panels, followed by the United States with 101, Portugal with 92, and Belgium with 85, while the remaining panels were distributed across another 72 countries and territories. Industry analysts noted that these figures represent accessible IP addresses rather than an exact count of physical supermarkets, as a single IP address can control multiple systems, meaning the data serves as a baseline estimate derived from IPv4 and specific port scans.
Historical scanning data demonstrates that these control panels were not suddenly exposed immediately prior to the attacks. Weekly scans conducted by IPinfo dating back to late March revealed a consistent global exposure of approximately 2,464 to 2,622 Danfoss panels every week, with roughly half consistently situated in France. Of the 1,331 French panels detected in October scans, 1,019 had occupied the exact same IP addresses as far back as March 30, indicating that a significant portion of the hardware had remained directly exposed to the public internet for at least six months. Although the proportion of French devices running updated software crept upward from 14% in March to 24% by October, remediation remained sluggish.
IPinfo determined that approximately 85%, or 1,136 of the scanned French control panels, were operating software containing known security flaws. The vulnerability rate in other nations hovered at a comparable 84%, suggesting that the scale of the incident in France stemmed from the exceptionally high volume of internet-exposed equipment rather than a uniquely poor patching cadence compared to other regions. Among the vulnerable French hardware, 527 units were older legacy controllers that Danfoss had already designated as end-of-life and unsupported. An additional 280 units lacked security patches released in 2023, while 329 units missed updates issued in 2025. The discontinued AK-SM 800 series reached its end-of-life status in 2023, the same year security researchers publicly detailed login-bypass vulnerabilities affecting the architecture, though newer controllers that failed to receive corresponding firmware updates remained equally susceptible to missing subsequent patches.
In the wake of the attacks, the volume of publicly exposed panels plummeted rapidly. A subsequent IPinfo scan on October 14 identified only 316 of the original 1,331 French IP addresses still online, representing a sudden reduction of roughly 76%. The count of unsupported legacy controllers dropped from 527 down to 64, while even fully updated devices fell from 195 to 54. Based on this sudden drop-off, investigators assessed that many supermarket operators likely severed public internet connections entirely rather than completing software updates. A separate internet scanning organization, Censys, independently observed a sharp decline in relevant panels across France, though pockets of legacy equipment remained exposed.
France’s national cybersecurity agency, CERT-FR, issued warnings that malicious activity targeting industrial refrigeration control systems could remain ongoing. The agency advised operators to immediately remove direct public internet access from all such devices, shifting remote maintenance protocols to secure virtual private networks or protected local architectures. For Danfoss hardware specifically, operators were urged to update firmware, configure security settings to a strict level, and replace default administrator passwords. Authorities stressed that operators must also conduct thorough audits of device configurations, particularly automated defrost schedules, and cautioned that a simple factory reset is insufficient to mitigate risks because unsupported, unpatchable hardware remains vulnerable to repeat compromises.
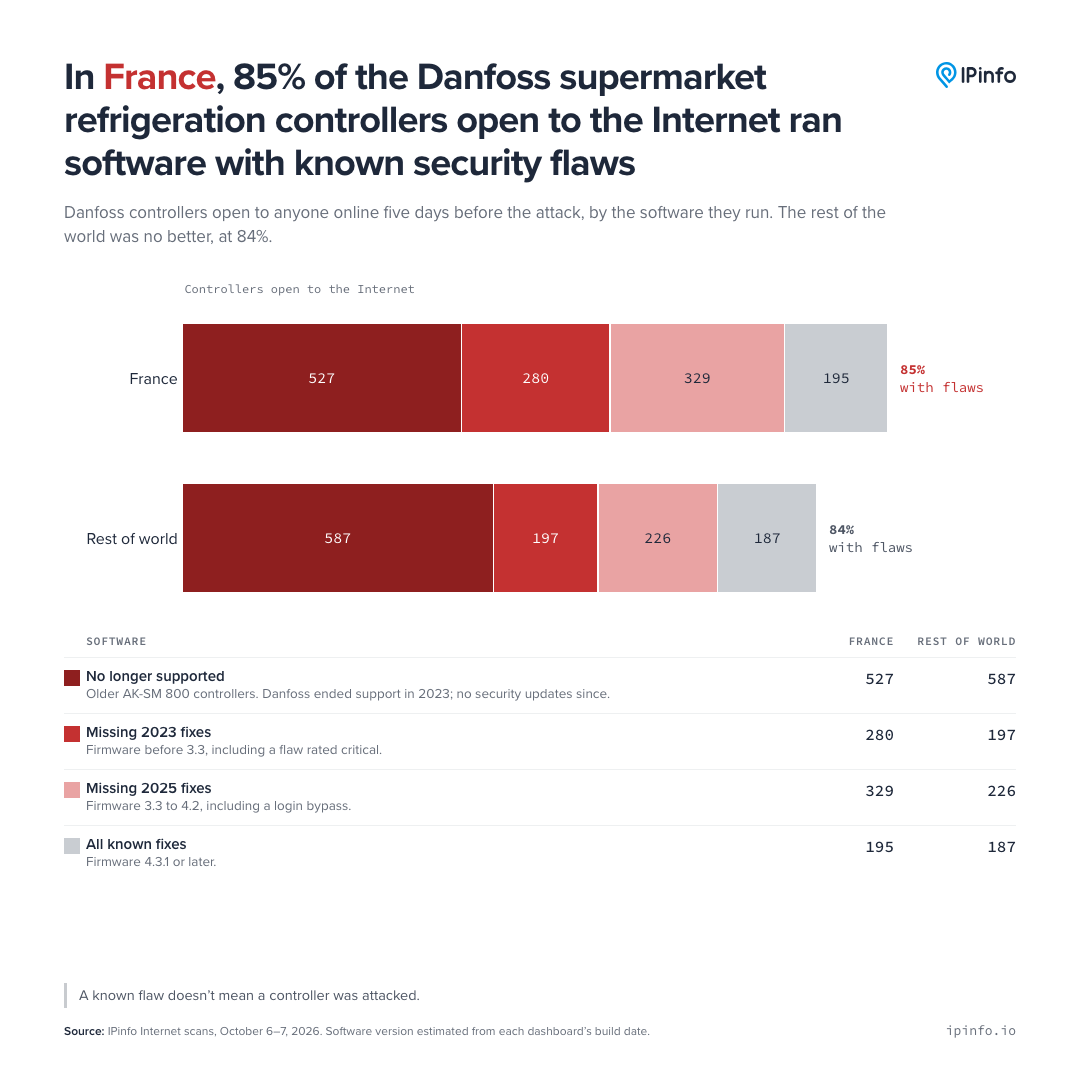
While scanning data highlights the widespread exposure of aging industrial equipment, cybersecurity analysts emphasize a distinction between public accessibility and confirmed exploitation. IPinfo clarified that its scans measure exposure and approximate software versions rather than serving as definitive proof that specific known vulnerabilities served as the primary entry point for the supermarket attacks, nor do the scans confirm exactly which individual retail locations were breached. Nevertheless, direct internet exposure combined with unpatched legacy firmware significantly elevates systemic operational risks for critical commercial refrigeration infrastructure.